Trezor Faces Another Data Breach After Shipping Partner Skladon Is Hacked
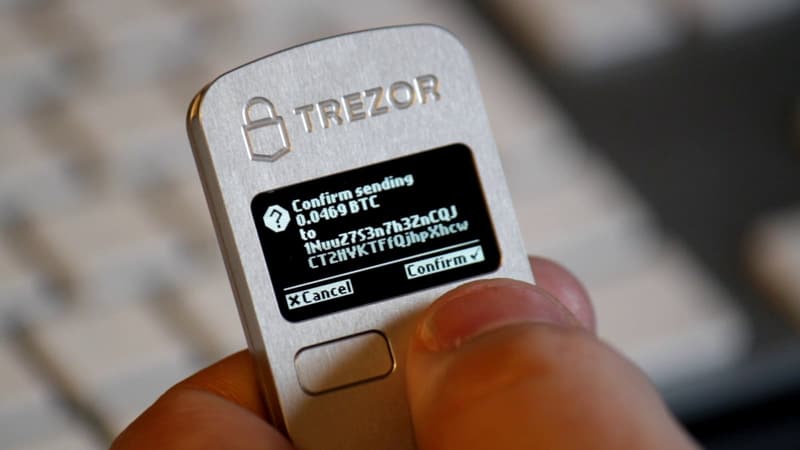
Representative photo · Photo: The original uploader was Ladislav Mecir / Wikimedia Commons, CC BY-SA 3.0
Hardware wallet maker Trezor experienced its second shipping partner breach in three months, exposing customer order records.
This is news, not investment advice. NexVani Media is not a SEBI-registered investment adviser and does not recommend buying or selling any security. Do your own research or consult a registered adviser before investing.
Hardware wallet maker Trezor has confirmed a security breach affecting one of its shipping partners, leading to another exposure of customer details. The incident marks the third third-party security failure for the company in a little over three months, resetting its internal monitoring counter to zero.
According to a company disclosure, malicious actors gained access to the systems of logistics partner Skladon on November 7. While the intrusion happened earlier, Skladon did not notify Trezor until November 15. The compromised records involve hardware-wallet purchases made between August 9 and November 7. The exported data includes buyers' full names, telephone numbers, delivery addresses, email addresses, and the specific products and prices associated with each transaction.
Trezor emphasized that its internal infrastructure remained secure, confirming that no wallet backups, PIN codes, or passphrases were accessed. The breach itself does not allow an unauthorized individual to transfer a user's funds directly. However, it provides malicious actors with a combination of personal home addresses and proof that individuals bought devices designed to store a bitcoin wallet. The company noted that US buyers were unaffected because Skladon does not handle shipments to the United States.
Following the discovery, some customers have already reported receiving fraudulent phone calls. Fraudsters can leverage exact model and pricing data to make unsolicited messages or calls appear authentic, or utilize home addresses to target individuals known to hold digital assets. To mitigate future risks, Trezor introduced anonymous parcel locker pickups across 18 European countries and is working to reduce order data retention from 90 to 45 days for itself and its shipping partners.
A breach at shipping partner Skladon exposed order details for approximately 27,000 Trezor customers.
## Why it matters
This incident highlights the growing risks associated with third-party supply chain dependencies in the digital asset sector. While companies like Trezor rely on external logistics providers to handle global distribution efficiently, repeated breaches underscore how vulnerable customer privacy can be even when core corporate infrastructure remains secure. For users, the fallout extends beyond digital security into physical privacy risks, as exposed delivery addresses and purchase records can be exploited by bad actors for targeted scams and offline threats.
Sources
More like this
Binance Hack May Shift Institutional Crypto Trading Toward Outside Custody
Luxor CEO Blames AI-Enabled Hackers for Bitcoin Mining Reward Redirection
Strategy Spends $1.4B on STRC Preferred Stock Recovery