Trezor Increases Passphrase Limit Following Trezor Coldcard Security Concerns
Representative photo · Photo: The original uploader was Ladislav Mecir / Wikimedia Commons, CC BY-SA 3.0
Hardware wallet manufacturer Trezor has extended its passphrase limit to 128 characters, pointing to security incidents involving Trezor and Coldcard.
This is news, not investment advice. NexVani Media is not a SEBI-registered investment adviser and does not recommend buying or selling any security. Do your own research or consult a registered adviser before investing.
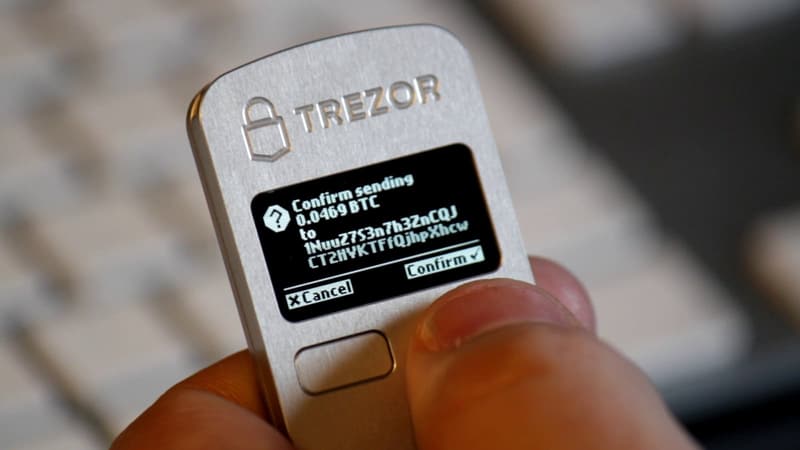
Hardware wallet manufacturer Trezor has upgraded its security features by raising the maximum allowed length for optional wallet passphrases from 50 to 128 characters. Announced on Sunday, the update is currently accessible through the Trezor Suite alongside updated device firmware, while older firmware versions will maintain the previous 50-character limit. A passphrase functions as an extra layer of protection set in addition to a standard recovery phrase. Even if an unauthorized party gains access to a user's recovery phrase, they would still require the correct passphrase to unlock the funds stored inside that wallet. Trezor highlighted security issues such as a comparison involving Trezor Coldcard incidents from July, where a firmware vulnerability caused certain devices to produce recovery phrases lacking adequate randomness, enabling attackers to rebuild them. Strong and unique passphrases successfully shielded several affected users during those events. ## Trezor Coldcard Security Warning This recent enhancement arrives alongside a separate alert concerning hardware security. On Friday, the company advised clients who purchased wallets through a former authorized reseller named CryptoBilis starting in March to transfer their assets into newly created wallets immediately. An Indonesian consumer identified a suspected listening device inside a Trezor Safe 5 model. This hidden component was capable of capturing on-screen data, including recovery phrases, and transmitting the information via a cellular network. Trezor stated on Friday that it had not yet inspected the specific device and noted zero reports concerning related financial losses. > Trezor raised its passphrase length limit to 128 characters following recent security vulnerabilities. ## Why it matters This modification gives cryptocurrency holders the ability to create significantly longer and more complex passphrases, offering enhanced defense against unauthorized access if recovery details are exposed. It underscores the ongoing necessity for robust physical and digital security measures across the digital asset ecosystem.
Sources
More like this
Solana Validators Urged to Patch Critical Linux Vulnerability