Cheap online services routed web traffic through White House network
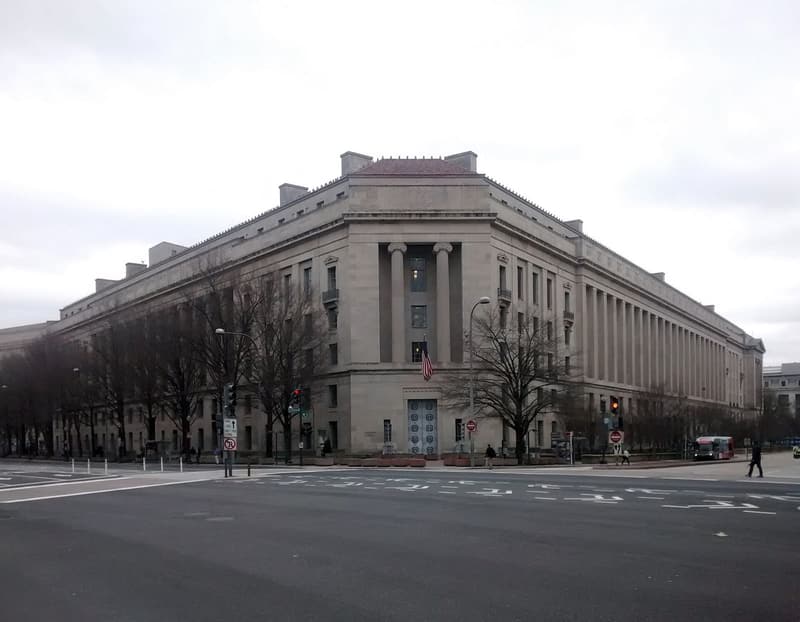
Representative photo · Photo: Sean McCue / Wikimedia Commons, CC BY-SA 2.5
Researchers report that affordable residential proxy services repeatedly directed external web traffic through a network linked to the White House.
This is news, not investment advice. NexVani Media is not a SEBI-registered investment adviser and does not recommend buying or selling any security. Do your own research or consult a registered adviser before investing.
A threat-intelligence firm has reported that inexpensive online services repeatedly routed web traffic through a network associated with the White House. According to Layer3 Intel, the company recorded 236 observations between October 5 and November 3 across six distinct internet addresses and 28 different services. This activity has generated discussions regarding the use of government-linked internet infrastructure by external entities.
The organization identified the involved network as hosting White House connectivity, noting that AS2650 is registered under EOP-ASN in ARIN records. However, this registration details neither the specific device nor the individual behind any given connection. Layer3 explained that residential proxy services sell customers access to external device internet connections, causing routed traffic to appear as though it originates from that specific network rather than the user's actual location.
During its monitoring window, Layer3 observed exits on 26 out of 30 days. The firm stated that its pipeline encountered the network while requesting global rotating access through residential proxy services rather than deliberately targeting AS2650. Furthermore, the company noted that similar access can be obtained by any member of the public willing to pay a small fee to a residential proxy provider.
Understanding cheap white paint and network exits
Layer3 cross-checked the IP addresses against public context pages from proxy-detection firms Spur and Synthient, which also classified them as residential proxy exits. The firm withheld the specific addresses in its published findings due to sensitivity. The captured figures describe recorded exits and proxy services but do not confirm the total number of devices involved or establish that every observation constituted a malicious attack.
Analysis of the timing showed that approximately half of the activity occurred between 5 p.m. and midnight Eastern time, with minimal activity during the early morning hours. Layer3 interpreted this pattern as indicative of an individual device running proxy software rather than a public guest Wi-Fi network. The firm suggested an infected device operating with a proxy software development kit as a potential explanation, while conceding that its data lacks device or user identification.
Inexpensive online services routed external web traffic through a White House-linked network multiple times.
Why it matters
The findings highlight potential security implications regarding poorly secured proxy software, which can occasionally expose internal systems if specific software development kit flaws are present. However, the published observations do not demonstrate actual unauthorized access to internal White House systems, and the data remains unreviewed by external raw log auditors.
As researchers continue to examine how residential proxy networks interact with government-linked infrastructure, the situation emphasizes the broader security challenges associated with commercially available routing services and third-party software integrations.
Sources
More like this
Ethereum Devs Delay Glamsterdam Hoodi Fork Over Security Concerns
NYSE-Backed Crypto Venture Faces 90% Stock Rejection Amid Liquidity Hurdles
Binance Security Incident Linked to Months of Prior Access